


Wydawcy
Katalog tematyczny
- Archeologia (109)
- Ekonomia, finanse, business (13704)
- Filozofia (1445)
- Historia (3040)
- Języki i językoznawstwo (2356)
- Lifestyle, hobby i rozrywka (475)
- Medycyna (9704)
- Nauki humanistyczne (4)
- Nauki o Ziemi i środowisku (2638)
- Nauki ścisłe (20412)
- Nauki społeczne (8486)
- Nauki techniczne (13450)
- Prawo (1696)
- Publikacje informacyjne i interdyscyplinarne (1288)
- Religia i wierzenia (917)
- Technika komputerowa (4067)
- Bazy danych (75)
- Bezpieczeństwo komputerowe (454)
- Certyfikacja komputerowa (1)
- Grafika i media cyfrowe (32)
- Informatyka (779)
- Komputery, ogólnie (74)
- Programowanie (351)
- Programy komercyjne (49)
- Sieci komputerowe (350)
- Sprzęt komputerowy (4)
- Systemy operacyjne (32)
- Technika cyfrowa na co dzień (7)
- Zdrowie, relacje międzyludzkie i rozwój osobisty (657)



Informacje szczegółowe o książce
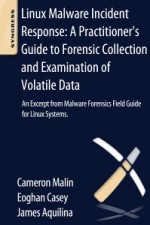
Linux Malware Incident Response: A Practitioners Guide to Forensic Collection and Examination of Volatile Data: An Excerpt from Malware Forensic Field Guide for Linux Systems
ISBN 9780124095076
Autor: Malin, Cameron H.Casey, EoghanAquilina, James M.
Wydawca: Elsevier
Dostępność: 3-6 tygodni
Cena: 126,00 zł
Przed złożeniem zamówienia prosimy o kontakt mailowy celem potwierdzenia ceny.
ISBN13: |
9780124095076 |
ISBN10: |
0124095070 |
Autor: |
Malin, Cameron H.Casey, EoghanAquilina, James M. |
Oprawa: |
Paperback |
Rok Wydania: |
2013-03-11 |
Tematy: |
UR |
Linux Malware Incident Response is a "first look" at the Malware Forensics Field Guide for Linux Systems, exhibiting the first steps in investigating Linux-based incidents. The Syngress Digital Forensics Field Guides series includes companions for any digital and computer forensic investigator and analyst. Each book is a "toolkit" with checklists for specific tasks, case studies of difficult situations, and expert analyst tips. This compendium of tools for computer forensics analysts and investigators is presented in a succinct outline format with cross-references to supplemental appendices. It is designed to provide the digital investigator clear and concise guidance in an easily accessible format for responding to an incident or conducting analysis in a lab.
Presented in a succinct outline format with cross-references to included supplemental components and appendicesCovers volatile data collection methodology as well as non-volatile data collection from a live Linux systemAddresses malware artifact discovery and extraction from a live Linux system
Introduction
Malware Incident Response: A Practitioner’s Guide to Volatile Data Collection and Examination on a Live Linux System
Appendix A: Linux Field Guide Tool Box
Appendix B: Selected Readings
Appendix C: Interview Questions
Appendix D: Pitfalls to Avoid
Appendix E: Live Response Field Notes
Koszyk
Książek w koszyku: 0 szt.
Wartość zakupów: 0,00 zł
Informacje


Kontakt
Gambit
Centrum Oprogramowania
i Szkoleń Sp. z o.o.
Al. Pokoju 29b/22-24
31-564 Kraków
Siedziba Księgarni
ul. Kordylewskiego 1
31-542 Kraków
+48 12 410 5991
+48 12 410 5987
+48 12 410 5989
Subskrypcje
Administratorem danych osobowych jest firma Gambit COiS Sp. z o.o. Na podany adres będzie wysyłany wyłącznie biuletyn informacyjny.
Autoryzacja płatności

Informacje na temat autoryzacji płatności poprzez PayU.
© Copyright 2012: GAMBIT COiS Sp. z o.o. Wszelkie prawa zastrzeżone.
Projekt i wykonanie: Alchemia Studio Reklamy