


Wydawcy
Katalog tematyczny
- Archeologia (109)
- Ekonomia, finanse, business (13704)
- Filozofia (1445)
- Historia (3040)
- Języki i językoznawstwo (2356)
- Lifestyle, hobby i rozrywka (475)
- Medycyna (9704)
- Nauki humanistyczne (4)
- Nauki o Ziemi i środowisku (2638)
- Nauki ścisłe (20412)
- Nauki społeczne (8486)
- Nauki techniczne (13450)
- Budownictwo lądowe (1045)
- Chemia przemysłowa (2258)
- Elektronika i telekomunikacja (3287)
- Energetyka (1122)
- Inne nauki stosowane (363)
- Inżynieria biochemiczna (507)
- Inżynieria transportu (232)
- Mechanika i materiały (3316)
- Nauka o środowisku (321)
- Rolnictwo (507)
- Technika, ogólnie (475)
- Prawo (1696)
- Publikacje informacyjne i interdyscyplinarne (1288)
- Religia i wierzenia (917)
- Technika komputerowa (4067)
- Zdrowie, relacje międzyludzkie i rozwój osobisty (657)





Informacje szczegółowe o książce
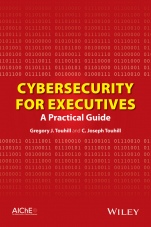
Cybersecurity for Executives: A Practical Guide
ISBN 9781118888148
Autor: Gregory J. Touhill, C. Joseph Touhill
Wydawca: Wiley
Dostępność: 3-6 tygodni
Cena: 473,55 zł
Przed złożeniem zamówienia prosimy o kontakt mailowy celem potwierdzenia ceny.
ISBN13: |
9781118888148 |
ISBN10: |
1118888146 |
Autor: |
Gregory J. Touhill, C. Joseph Touhill |
Oprawa: |
Hardback |
Rok Wydania: |
2014-06-18 |
Ilość stron: |
416 |
Wymiary: |
243x163 |
Tematy: |
TDCB |
This book is the essential cybersecurity text for executives in every corporate level and sector. Equally applicable to board members, CEOs and other C–suite officers, and others with leadership and managerial responsibilities, it gives practical advice that equips executives with the knowledge they need to make the right cybersecurity decisions. Written as a Practical Guide, the book explains in plain language how to recognize and act upon cybersecurity threats to protect yourself and your business, how to manage risk, and how to recover when a cyber incident occurs. It gives executives vital information needed to understand cybersecurity best practices and how to integrate them into their business to manage risk. Those who read this book will be better prepared to train their personnel, use cybersecurity metrics to protect their bottom line, and act decisively to mitigate and recover from cyber incidents. Through discussions of risk, strategy, policies, change and personnel management, and performance measures, the book provides relevant and timely information to help readers make better decisions regarding cybersecurity. An ideal book for business executives, it also is an important textbook for any computer science, engineering, or business curriculum at both the undergraduate and graduate levels.
Preface Foreword Chapter 1. Introduction 1.1 Defining Cybersecurity 1.2 Cybersecurity is a Business Imperative 1.3 Cybersecurity is an Executive–Level Concern 1.4 Questions to Ask 1.5 Views of Others 1.6 Cybersecurity is a Full–Time Activity Chapter 2. Why Be Concerned? 2.1 A Classic Hack 2.2 Who Wants Your Fortune? 2.3 Nation State Threats 2.4 Cybercrime is Big Business 2.5 Chapter Summary Chapter 3. Managing Risk 3.1 Who Owns Risk In Your Business? 3.2 What Are Your Risks? 3.3 Calculating Your Risk 3.4 Communicating Risk 3.5 Organizing for Success 3.6 Chapter Summary Chapter 4. Build Your Strategy 4.1 How Much “Cybersecurity” Do I Need? 4.2 The Mechanics of Building Your Strategy 4.3 Avoiding Strategy Failure 4.4 Ways to Incorporate Cybersecurity into Your Strategy 4.5 Plan For Success 4.6 Chapter Summary Chapter 5. Plan for Success 5.1 Turning Vision Into Reality 5.2 Policies Complement Plans 5.3 Procedures Implement Plans 5.4 Exercise Your Plans 5.5 Legal Compliance Concerns 5.6 Auditing 5.7 Chapter Summary Chapter 6. Change Management 6.1 Why Managing Change is Important 6.2 When to Change? 6.3 What is Impacted by Change? 6.4 Change Management and Internal Controls 6.5 Change Management as a Process 6.6 Best Practices in Change Management 6.7 Chapter Summary Chapter 7. Personnel Management 7.1 Finding the Right Fit 7.2 Creating the Team 7.3 Establishing Performance Standards 7.4 Organizational Considerations 7.5 Training for Success 7.6 Special considerations for critical infrastructure protection 7.7 Chapter Summary Chapter 8. Performance Measures 8.1 Why Measure? 8.2 What to Measure? 8.3 Metrics and the C–Suite 8.4 The Executive Cybersecurity Dashboard 8.5 Chapter Summary Chapter 9. What To Do When You Get Hacked 9.1 Hackers already have you under surveillance 9.2 Things to do before tis too late: preparing for the hack 9.3 What to do when bad things happen: implementing your plan 9.4 Foot Stompers 9.5 Fool Me Once… 9.6 Chapter Summary Chapter 10. Boardroom Interactions Acknowledgements Appendix A – Policies Appendix B – General Rules for Email Etiquette Glossary Bibliography Index
Gregory J. Touhill , CISSP, is a Cybersecurity and Information Technology consultant, academic and author with nearly 30 years of experience creating, sustaining, and defending information technology solutions that are effective, efficient, and secure. An experienced CIO and certified professional director, his team was awarded the 2012 Rowlett Award by the National Security Agency. An adjunct professor at Washington University in St. Louis’ College of Engineering and Applied Science graduate programs in Cybersecurity and Information Management, he is engaged in several research projects with industry and academic partners, focusing on Cybersecurity issues. C. Joseph Touhill is a successful CEO, board member, and senior executive. He is highly experienced in creating and managing companies, both large and small. He has been a corporate officer for 41 years, 29 years of which he has been a CEO. Additionally, he has had extensive board and high–level committee experience.
Koszyk
Książek w koszyku: 0 szt.
Wartość zakupów: 0,00 zł
Informacje


Kontakt
Gambit
Centrum Oprogramowania
i Szkoleń Sp. z o.o.
Al. Pokoju 29b/22-24
31-564 Kraków
Siedziba Księgarni
ul. Kordylewskiego 1
31-542 Kraków
+48 12 410 5991
+48 12 410 5987
+48 12 410 5989
Subskrypcje
Administratorem danych osobowych jest firma Gambit COiS Sp. z o.o. Na podany adres będzie wysyłany wyłącznie biuletyn informacyjny.
Autoryzacja płatności

Informacje na temat autoryzacji płatności poprzez PayU.
© Copyright 2012: GAMBIT COiS Sp. z o.o. Wszelkie prawa zastrzeżone.
Projekt i wykonanie: Alchemia Studio Reklamy